An installed mobile application handles real-time odds and account controls differently from a browser tab, especially when connection stability fluctuates. 1xBet distributes its Android software as a standalone package rather than through the Play Store, which changes how you obtain, approve, and maintain the program on your device. This guide treats the entire process as a troubleshooting exercise: understanding what arrives on your phone, why Android objects, and how to respond without compromising the installation. Every decision point involves reading system messages accurately rather than tapping through warnings.
What the APK Actually Contains
The file reaching your phone is an Android Package, abbreviated APK, which bundles the betting interface, account management tools, casino modules, and payment gateways into a single installable archive. Unlike store-distributed apps that update through Google’s infrastructure, this package requires direct handling. The structure contains compiled code, asset files for graphics, and digital signatures verifying origin. When you trigger an install, Android unpacks this archive, checks those signatures against its security model, and allocates sandboxed storage for user data.
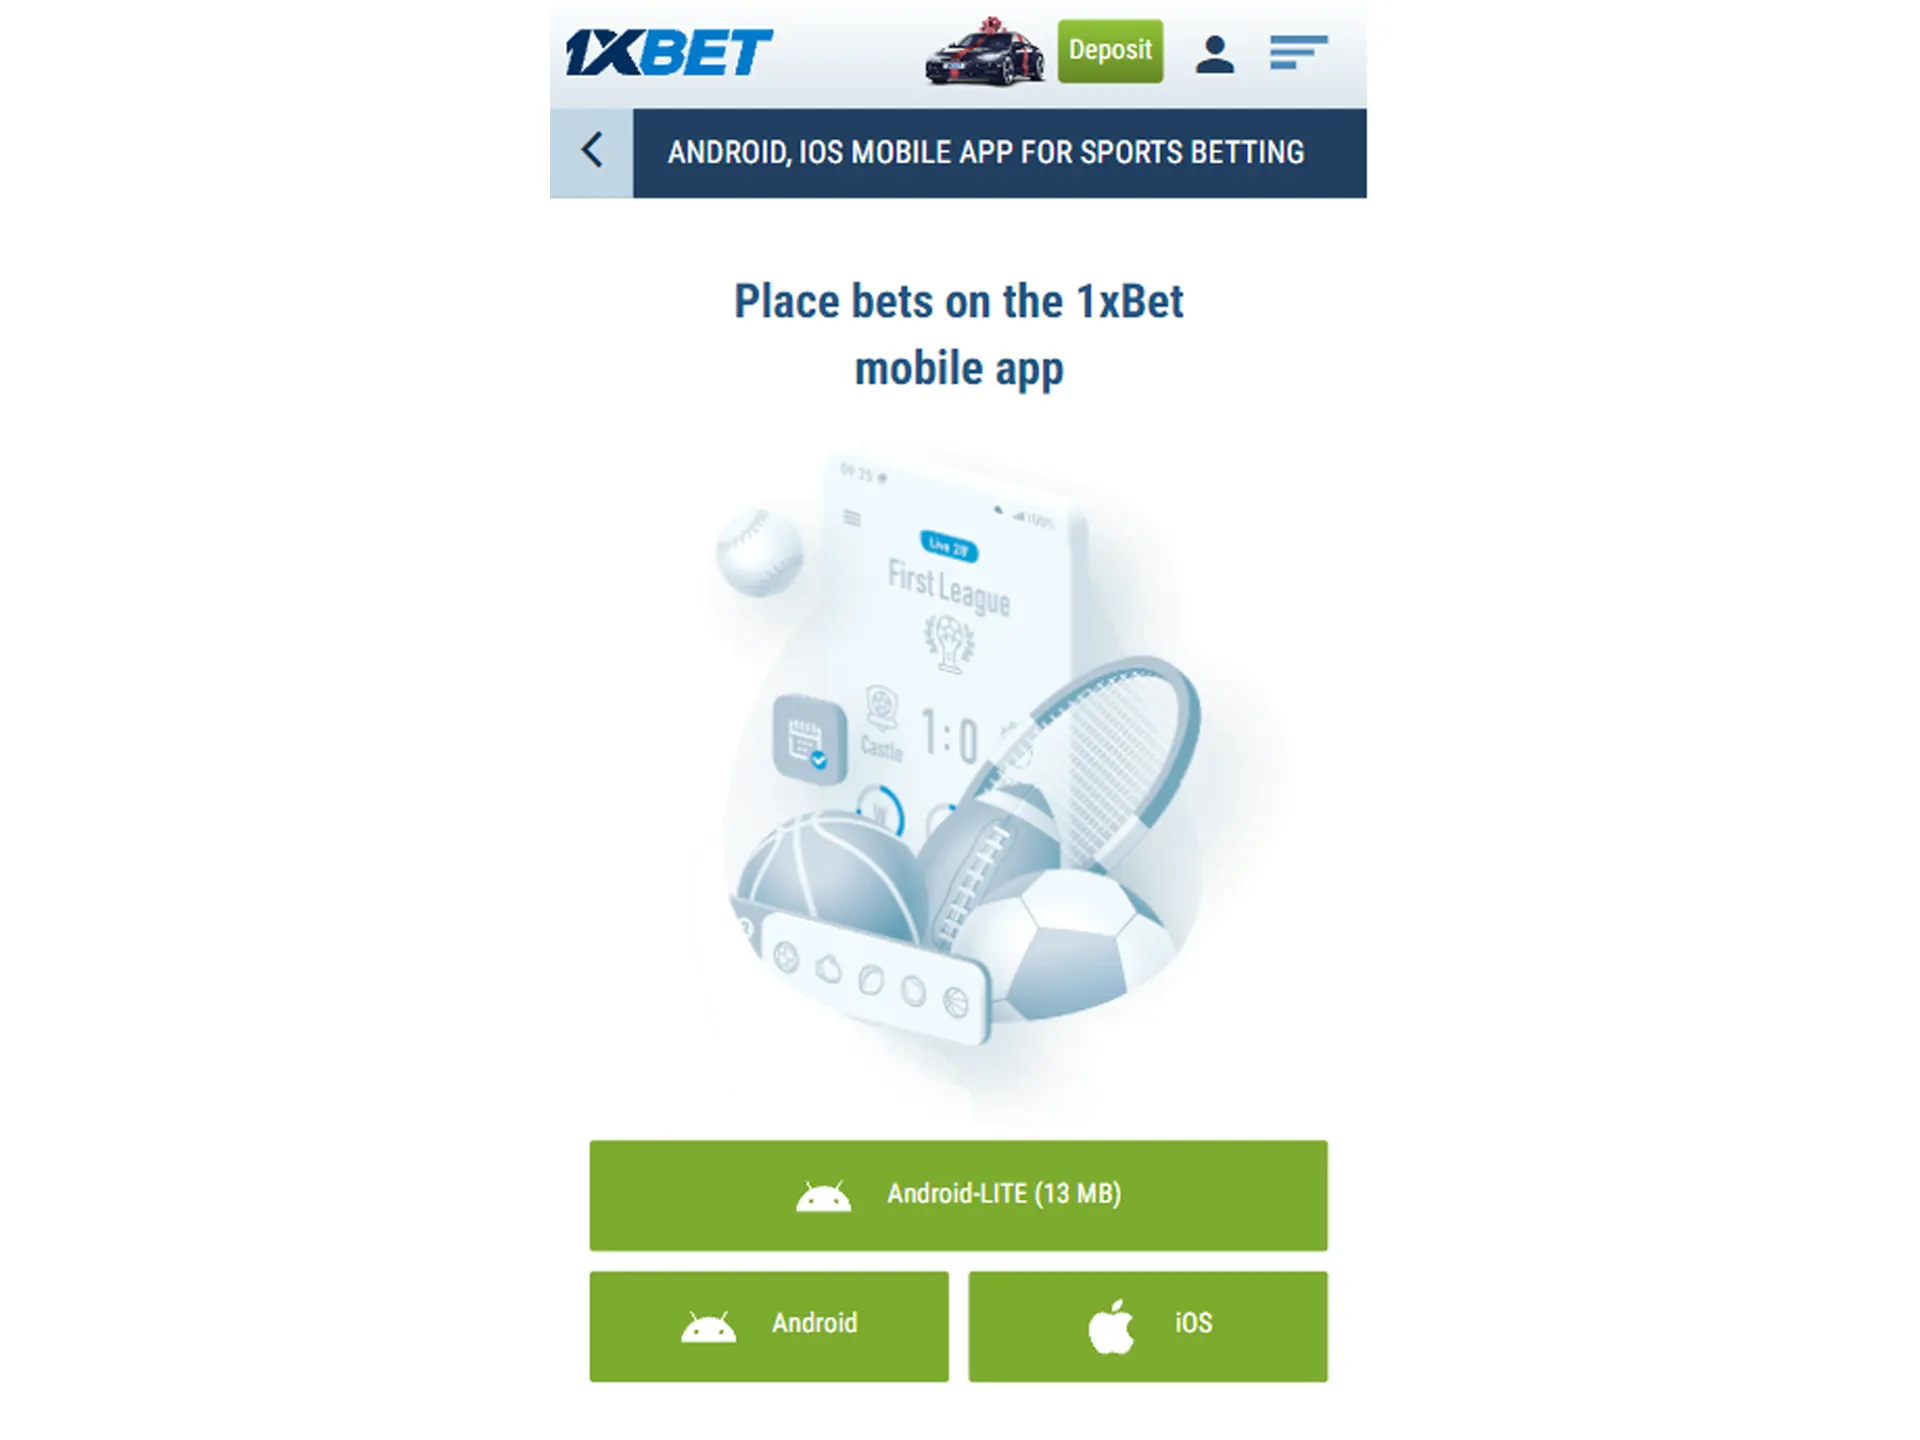
Source verification matters because Android cannot confirm the package came from a vetted distribution channel. The operating system defaults to suspicion when encountering software obtained outside its ecosystem. This protective stance triggers the warnings you will encounter, and understanding their nature prevents both unnecessary fear and careless override. The APK itself functions identically to a store version once installed, but the pathway to that state demands more attention.
Key distinctions between APK and Play Store distribution:
- Signature verification still occurs, but against the distributor’s certificate rather than Google’s
- Updates arrive as full replacement packages rather than incremental patches
- Storage permissions and background behavior follow identical rules once installed
- Uninstallation removes local data unless cloud backup was separately configured
Acquisition and Initial Setup Steps
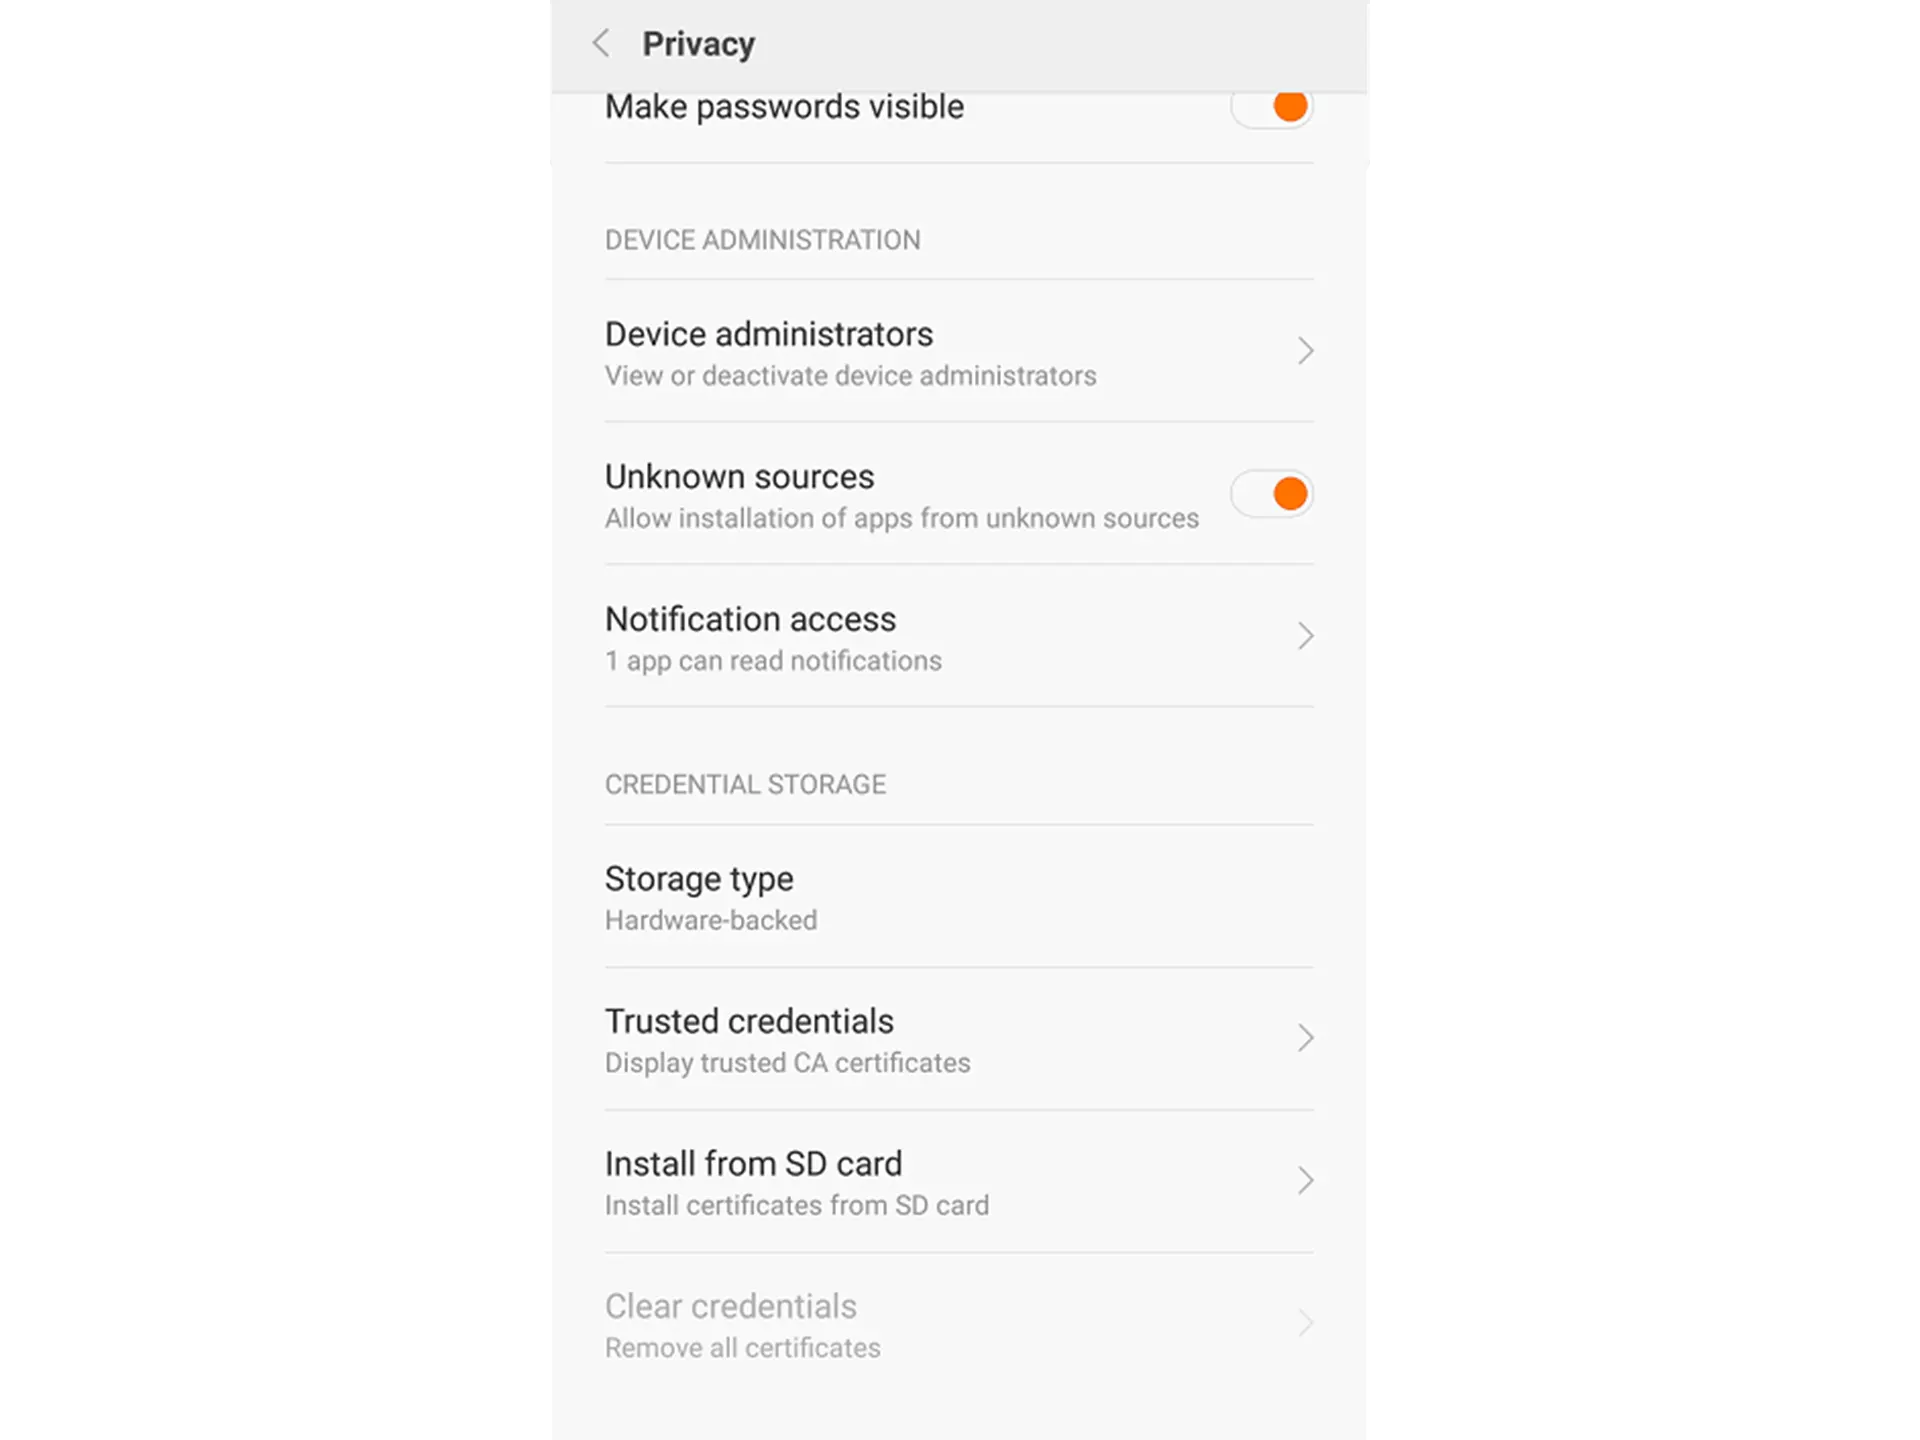
First, retrieve the package through direct download, typically initiated from the 1xBet website. Your browser will save the file to a default downloads directory. Before installation proceeds, Android requires explicit permission for that specific browser to install unknown applications—a setting found in system menus under Apps → Special Access → Install Unknown Apps. Grant this permission to your browser, complete the install, then revoke it if preferred; the installed application functions independently afterward.
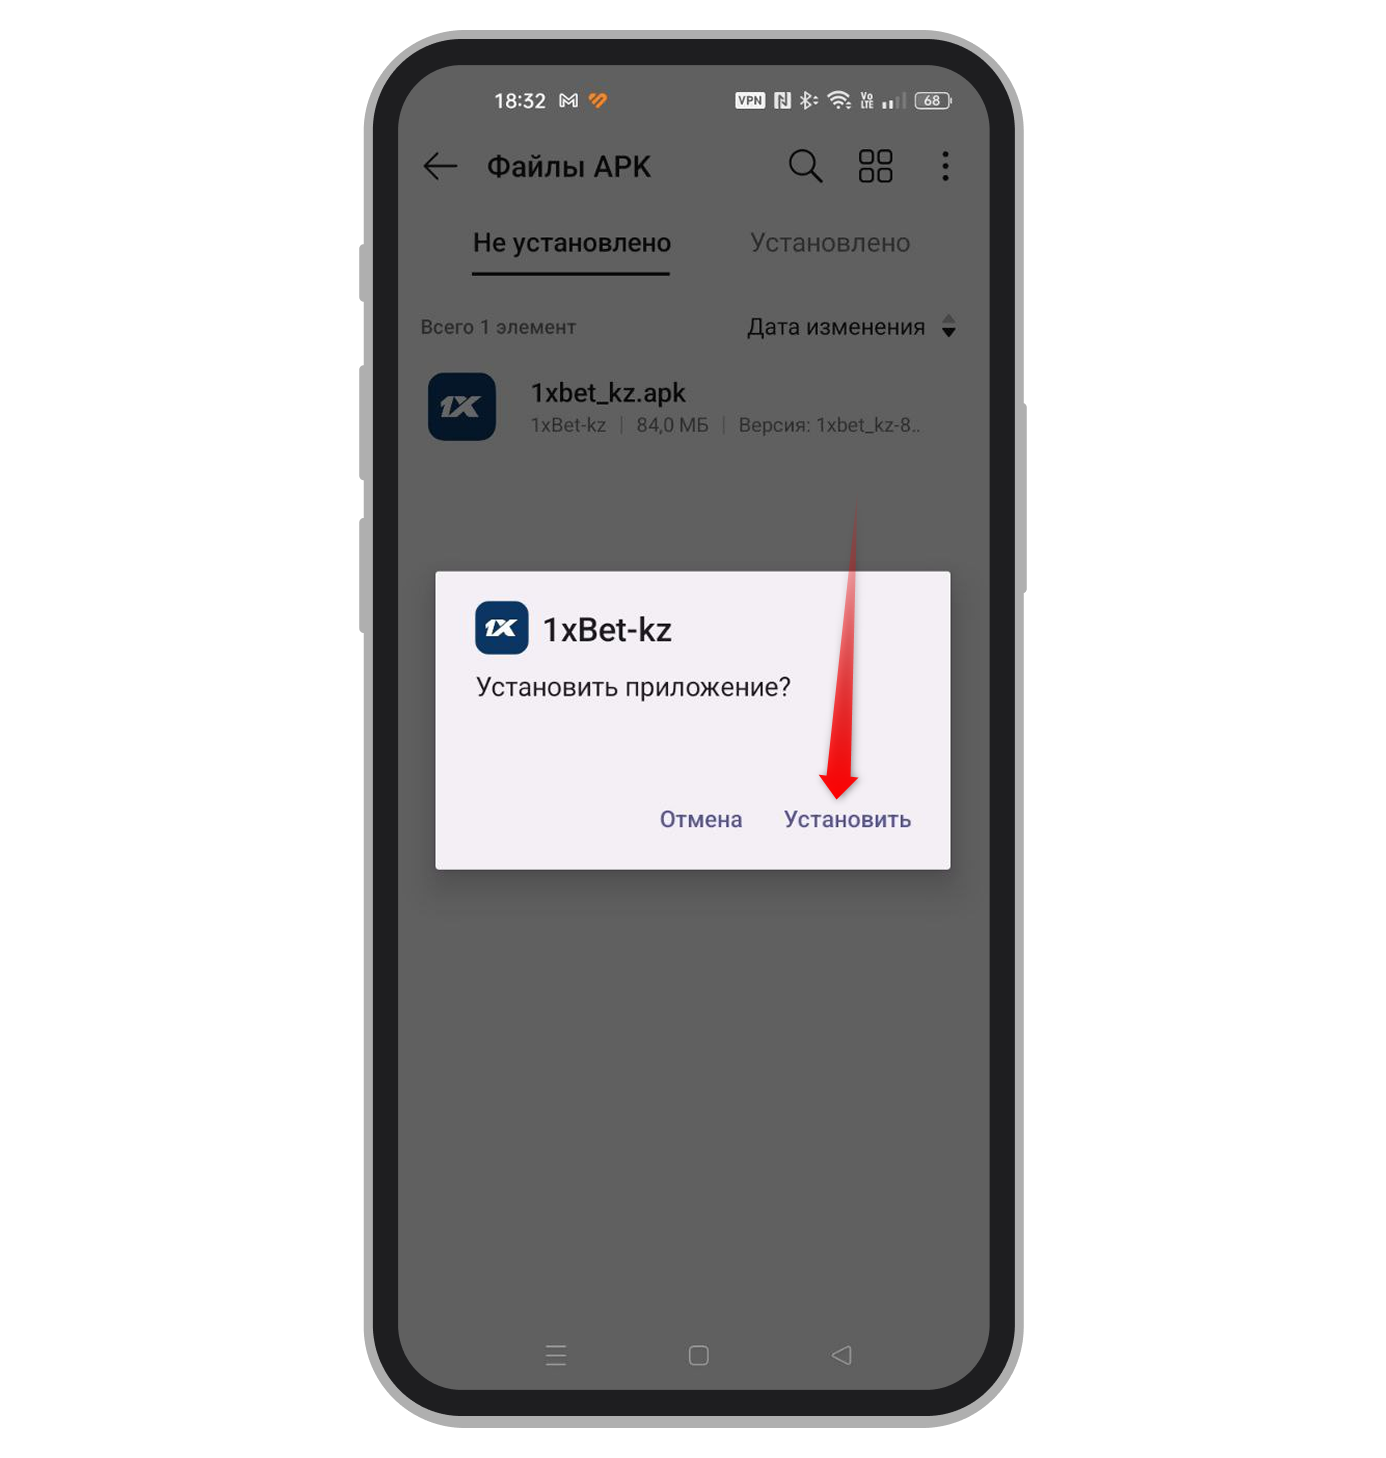
The 1xbet betting download setup file arrives with standard Android manifest declarations. When you tap the downloaded item, the system presents a parsing screen showing requested permissions. These mirror what any betting application requires: network access, storage for caching, possibly location if regional verification applies. Review these carefully rather than accepting automatically.
Installation sequence with mandatory checkpoints:
- Download completes; notification or file manager access required to locate
- Browser permission granted for one-time install authorization
- Android package parser analyzes APK structure and certificate
- Security dialog presents with explicit “Install anyway” option
- App launches or returns to home screen for manual opening
Decoding Android’s Security Dialogs
Android’s warning hierarchy progresses from informational to obstructive, and your response should vary accordingly. The initial “harmful” or “unrecognized developer” alert appears for every non-store APK. This does not indicate detection of malicious content; it reflects absence from Google’s developer registry. Read the specific language: phrases like “Play Protect doesn’t recognize this app” describe unfamiliarity, not danger. Tapping “More details” reveals the actual install button rather than dismissing the prompt.
More serious blocks occur when signature mismatches or corrupted packages trigger parsing failures. These prevent installation entirely rather than requesting override. Distinguishing between ” unrecognized” (proceedable) and “corrupt” or “invalid” (fatal) saves time and prevents repeated download attempts of damaged files. Certificate mismatches during updates—when the new APK carries a different signature than the installed version—similarly block with opaque error messages. Uninstalling the previous version becomes necessary, accepting total local data loss unless account information syncs server-side.
Common warning types and appropriate responses:
| Android Message |
Meaning |
Action |
| Play Protect warning, “Unknown developer” |
Standard for non-Play distribution |
Expand details, proceed if source verified |
| “App not installed” with no detail |
Signature conflict or version downgrade attempt |
Uninstall existing, reinstall fresh |
| “Parse error” |
Incomplete download or incompatible architecture |
Redownload, verify file size |
| Permission request loop |
Browser source not authorized |
Grant specific browser permission in system settings |
Post-install, Android may continue flagging the application in Play Protect scans. “Send app for scanning” requests can be declined; “uninstall harmful app” suggestions can be ignored if you intentionally installed from this verified source. These ongoing warnings represent persistent categorization, not new threat detection.
Maintenance and Alternative Access
Updates function through the same manual process: download new APK, install over existing, or uninstall-reinstall if signatures changed. Android remembers your previous permission grants per source, so subsequent installs from the same browser require less intervention. However, certificate rotation—uncommon but possible—forces clean installation with data reset. Regular backup of account credentials prevents lockout when local sessions expire.
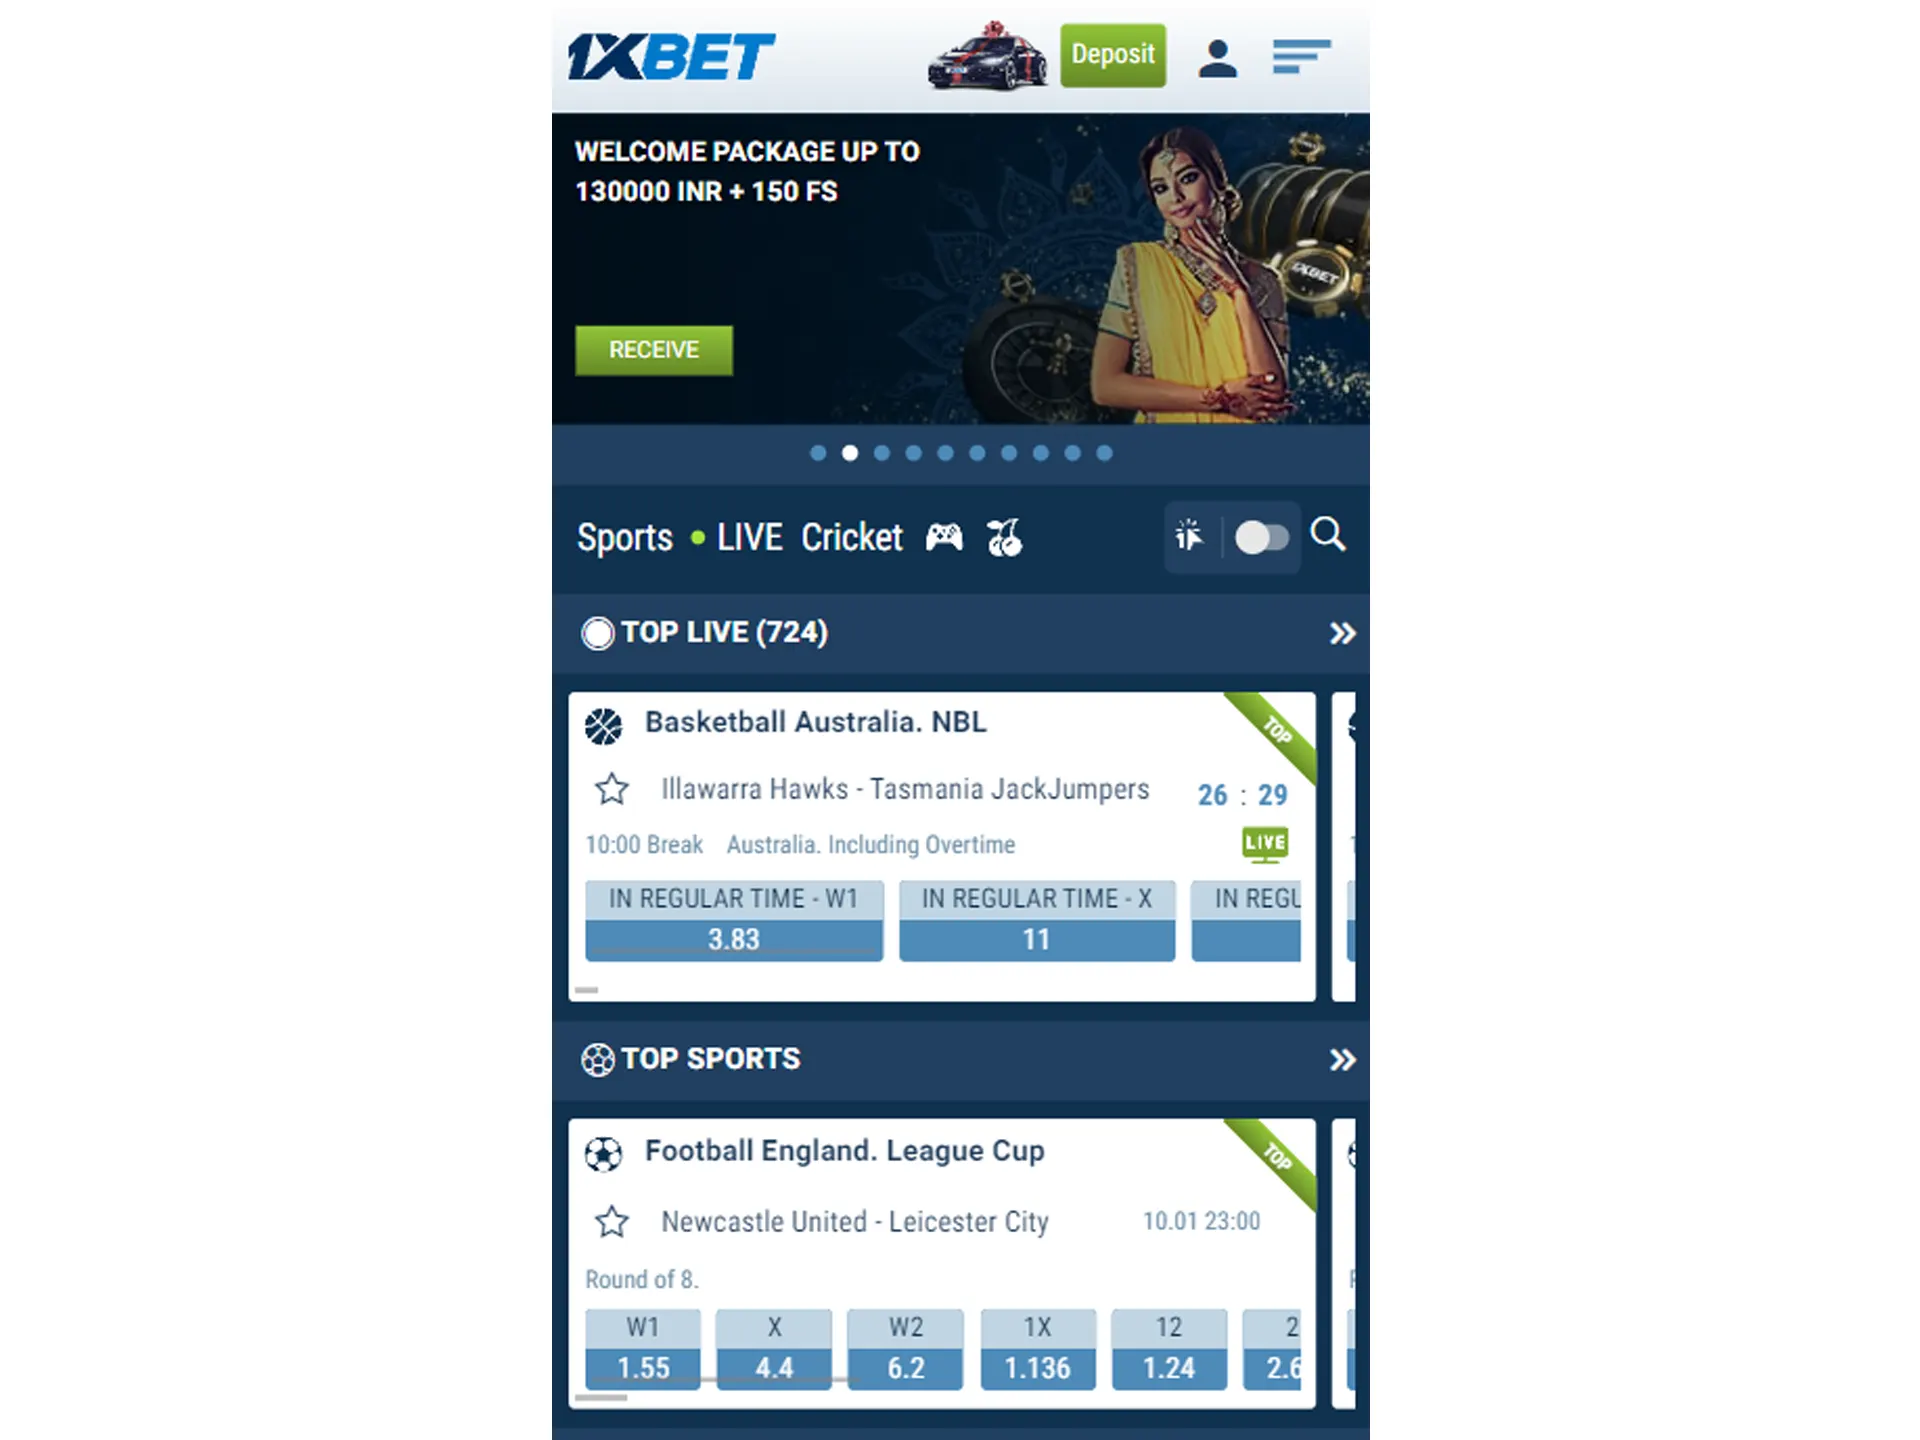
Core functionality available through both app and mobile site includes:
- Pre-match and live sports betting with real-time odds adjustment
- Casino verticals: slots, table games, live dealer streaming
- Payment processing: deposits, withdrawals, transaction history
- Account management: verification documents, bonus status, responsible gambling controls
- Push notifications for bet settlement and promotional alerts (app-only)
The mobile website serves as reliable fallback when installation fails or device storage is constrained. Modern browsers execute the responsive web application with near-native performance for betting and account functions. Only biometric login and push notifications require the installed package. Regional availability affects which interface displays; some jurisdictions present simplified versions automatically.
Gambling carries financial risk; establish deposit limits and session timers through account settings, and consult BeGambleAware if control becomes difficult. Self-exclusion tools function identically across app and web interfaces.
FAQ
Why does Android call the 1xBet app “harmful” when I’m certain of the source?
The warning reflects distribution channel, not content analysis. Play Protect labels all non-Play Store apps as unrecognized by default. “Harmful” in this context means “unverified by Google’s screening,” not “detected as malware.” The string appears for every sideloaded APK regardless of actual safety, and the operating system provides override pathways precisely because legitimate software distributes outside the store.
Should I disable Play Protect entirely to stop the warnings?
Disabling system-wide protection removes a layer of defense for all applications, not just this one. Instead, tap through the specific installation dialog when confident of source authenticity, then dismiss subsequent scan notifications without disabling the service entirely. Play Protect continues monitoring other software without constant interruption.
What does “App not installed” with no error code actually mean?
This generic failure typically indicates signature certificate mismatch between your installed version and the update file, or insufficient storage for the unpacked application. Uninstall the existing application—accepting that local data clears—and install the fresh APK. If the error persists, the download itself may be incomplete; verify file integrity through size comparison or re-download.
Why does the permission request appear for my browser rather than the betting app?
Android’s security model treats installation as a privileged action by the delivering application, not the payload being installed. Your browser or file manager requests authority to trigger installs; the betting app receives no special status. Granting this permission enables one installation, after which you may revoke it without affecting the installed program’s operation.
How do I know whether to trust an update notification?
Updates for this application do not arrive through Android’s standard notification channel. Any prompt claiming an available update that did not originate from your manual check of the source website should be treated as suspicious. Always initiate downloads directly from the verified distribution point rather than following links in unexpected messages or pop-ups.


1xBet App for Android: Reading Android’s Warnings Properly
An installed mobile application handles real-time odds and account controls differently from a browser tab, especially when connection stability fluctuates. 1xBet distributes its Android software as a standalone package rather than through the Play Store, which changes how you obtain, approve, and maintain the program on your device. This guide treats the entire process as a troubleshooting exercise: understanding what arrives on your phone, why Android objects, and how to respond without compromising the installation. Every decision point involves reading system messages accurately rather than tapping through warnings.
What the APK Actually Contains
The file reaching your phone is an Android Package, abbreviated APK, which bundles the betting interface, account management tools, casino modules, and payment gateways into a single installable archive. Unlike store-distributed apps that update through Google’s infrastructure, this package requires direct handling. The structure contains compiled code, asset files for graphics, and digital signatures verifying origin. When you trigger an install, Android unpacks this archive, checks those signatures against its security model, and allocates sandboxed storage for user data.
Source verification matters because Android cannot confirm the package came from a vetted distribution channel. The operating system defaults to suspicion when encountering software obtained outside its ecosystem. This protective stance triggers the warnings you will encounter, and understanding their nature prevents both unnecessary fear and careless override. The APK itself functions identically to a store version once installed, but the pathway to that state demands more attention.
Key distinctions between APK and Play Store distribution:
Acquisition and Initial Setup Steps
First, retrieve the package through direct download, typically initiated from the 1xBet website. Your browser will save the file to a default downloads directory. Before installation proceeds, Android requires explicit permission for that specific browser to install unknown applications—a setting found in system menus under Apps → Special Access → Install Unknown Apps. Grant this permission to your browser, complete the install, then revoke it if preferred; the installed application functions independently afterward.
The 1xbet betting download setup file arrives with standard Android manifest declarations. When you tap the downloaded item, the system presents a parsing screen showing requested permissions. These mirror what any betting application requires: network access, storage for caching, possibly location if regional verification applies. Review these carefully rather than accepting automatically.
Installation sequence with mandatory checkpoints:
Decoding Android’s Security Dialogs
Android’s warning hierarchy progresses from informational to obstructive, and your response should vary accordingly. The initial “harmful” or “unrecognized developer” alert appears for every non-store APK. This does not indicate detection of malicious content; it reflects absence from Google’s developer registry. Read the specific language: phrases like “Play Protect doesn’t recognize this app” describe unfamiliarity, not danger. Tapping “More details” reveals the actual install button rather than dismissing the prompt.
More serious blocks occur when signature mismatches or corrupted packages trigger parsing failures. These prevent installation entirely rather than requesting override. Distinguishing between ” unrecognized” (proceedable) and “corrupt” or “invalid” (fatal) saves time and prevents repeated download attempts of damaged files. Certificate mismatches during updates—when the new APK carries a different signature than the installed version—similarly block with opaque error messages. Uninstalling the previous version becomes necessary, accepting total local data loss unless account information syncs server-side.
Common warning types and appropriate responses:
Post-install, Android may continue flagging the application in Play Protect scans. “Send app for scanning” requests can be declined; “uninstall harmful app” suggestions can be ignored if you intentionally installed from this verified source. These ongoing warnings represent persistent categorization, not new threat detection.
Maintenance and Alternative Access
Updates function through the same manual process: download new APK, install over existing, or uninstall-reinstall if signatures changed. Android remembers your previous permission grants per source, so subsequent installs from the same browser require less intervention. However, certificate rotation—uncommon but possible—forces clean installation with data reset. Regular backup of account credentials prevents lockout when local sessions expire.
Core functionality available through both app and mobile site includes:
The mobile website serves as reliable fallback when installation fails or device storage is constrained. Modern browsers execute the responsive web application with near-native performance for betting and account functions. Only biometric login and push notifications require the installed package. Regional availability affects which interface displays; some jurisdictions present simplified versions automatically.
Gambling carries financial risk; establish deposit limits and session timers through account settings, and consult BeGambleAware if control becomes difficult. Self-exclusion tools function identically across app and web interfaces.
FAQ
Why does Android call the 1xBet app “harmful” when I’m certain of the source?
The warning reflects distribution channel, not content analysis. Play Protect labels all non-Play Store apps as unrecognized by default. “Harmful” in this context means “unverified by Google’s screening,” not “detected as malware.” The string appears for every sideloaded APK regardless of actual safety, and the operating system provides override pathways precisely because legitimate software distributes outside the store.
Should I disable Play Protect entirely to stop the warnings?
Disabling system-wide protection removes a layer of defense for all applications, not just this one. Instead, tap through the specific installation dialog when confident of source authenticity, then dismiss subsequent scan notifications without disabling the service entirely. Play Protect continues monitoring other software without constant interruption.
What does “App not installed” with no error code actually mean?
This generic failure typically indicates signature certificate mismatch between your installed version and the update file, or insufficient storage for the unpacked application. Uninstall the existing application—accepting that local data clears—and install the fresh APK. If the error persists, the download itself may be incomplete; verify file integrity through size comparison or re-download.
Why does the permission request appear for my browser rather than the betting app?
Android’s security model treats installation as a privileged action by the delivering application, not the payload being installed. Your browser or file manager requests authority to trigger installs; the betting app receives no special status. Granting this permission enables one installation, after which you may revoke it without affecting the installed program’s operation.
How do I know whether to trust an update notification?
Updates for this application do not arrive through Android’s standard notification channel. Any prompt claiming an available update that did not originate from your manual check of the source website should be treated as suspicious. Always initiate downloads directly from the verified distribution point rather than following links in unexpected messages or pop-ups.